It is unsettling to open a website log and find requests for files you never published. Many of these requests come from scanning bots: programs that search websites for known weaknesses. A request tells you that someone looked. It does not, by itself, tell you that someone got in.
Understand the idea
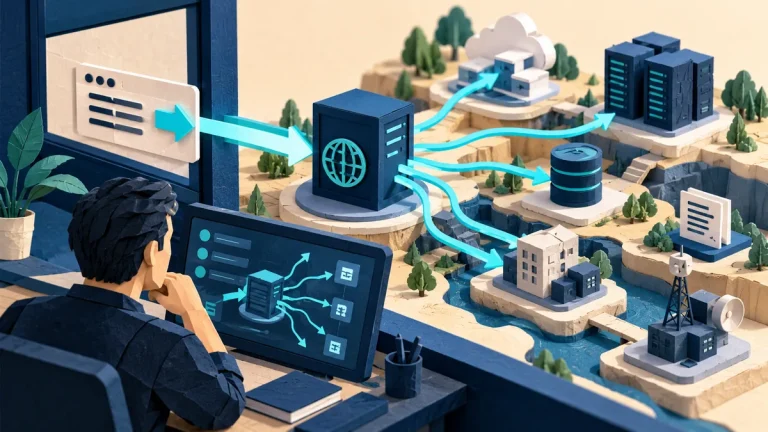
To understand the event, follow the exchange. The bot asks for a page or file, and your server sends a response. Check what the server actually returned. A successful status code can still lead to an ordinary error page. A large download of a real private file is a different matter.
- Request
Identify the path and the affected hostname.
- Response
Check the status, response size, and actual content.
- Outcome
Investigate access to real data; fix any exposure.
A practical example
Imagine a bot asking for an old database backup. The log records a successful response. Before declaring a breach, the website owner checks the deployment files and the size of the response. If the archive really was public, the team restricts access, keeps the logs, and checks what information the archive contained.
What to do next
- Confirm ownership. Separate your approved monitoring and security scans from unknown traffic using an inventory and scheduled scan records.
- Check the actual exposure. Review the configuration and file inventory on systems you own. Avoid opening suspicious files through the public website.
- Prioritize successful access. Escalate unexpected downloads, authentication successes, uploads, or changes to executable files. Repeated blocked requests alone usually have lower urgency.
- Close the opening. Remove public backups, patch affected components, restrict management interfaces, and stop code execution in upload directories where the application does not need it.
- Tune the edge carefully. Rate limits and web application firewall rules can reduce abusive traffic. Test ordinary users, integrations, and approved scanners before tightening them.
How to check the result
A useful result is evidence that the private file is no longer reachable and the normal website still works. If the file contained passwords or keys, replacing those secrets is a separate task.
The request returned HTTP 200. Does that prove a breach?
No. Some error pages also return 200. Compare the response with the expected application behavior and preserve the relevant logs before deciding what was accessed.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.