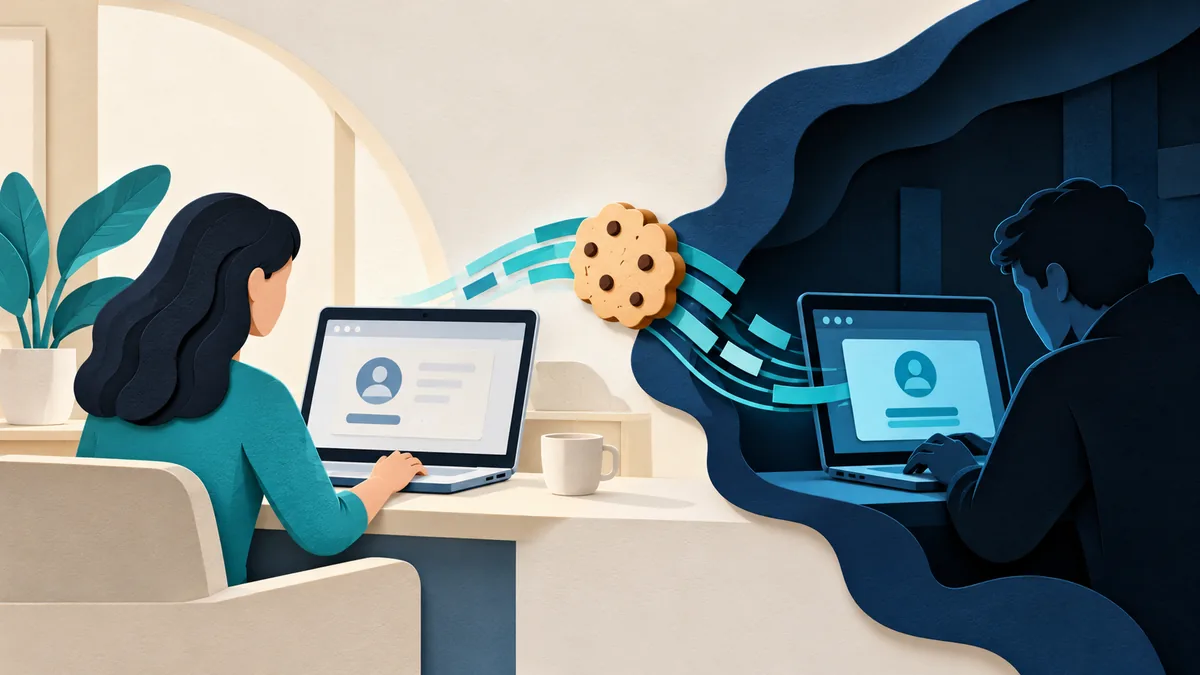
A website usually keeps you signed in with a session cookie, a small piece of browser data linked to your login. If someone steals that session information, they may be able to use the account without entering your password again. This is why a password change may not solve every account takeover.
Understand the idea
A password proves your identity at sign-in. A session lets the service remember that proof afterwards. Different providers handle sessions differently when a password changes. You may need a separate sign-out-everywhere action, and connected applications may have their own access to remove.
- Sign-in
A legitimate session is established.
- Theft
A copied session may be used without a new password prompt.
- Containment
Revoke sessions and inspect the device and connected access.
A practical example
For example, a staff member changes a compromised password but later sees another unauthorized message. Support finds an active session that was not ended by the reset. The team removes that session, checks connected applications and recovery details, and investigates the device that may have exposed the cookie.
What to do next
- Use appropriate cookie controls. Secure limits transport to HTTPS; HttpOnly prevents ordinary JavaScript from reading the cookie. Choose SameSite behavior to fit the application's flows. These controls have different purposes and do not neutralize endpoint malware.
- Rotate session identifiers at trust changes. Establish a fresh session after authentication and privilege changes. Avoid putting tokens in URLs or logs.
- Bound lifetime. Set idle and absolute timeouts appropriate to the data and workflow. Sensitive actions may need fresh authentication.
- Make revocation real. Define what sign-out, password reset, device removal, and “sign out everywhere” invalidate. Include refresh tokens and connected application grants where relevant.
How to check the result
Confirm that the unwanted session no longer works. Also check how it was stolen; otherwise, the same device or extension may expose the next session too.
I changed the password. Can I assume the attacker is out?
Verify session revocation and review connected applications and recovery details. The provider’s controls determine which sessions a password change actually ends.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.