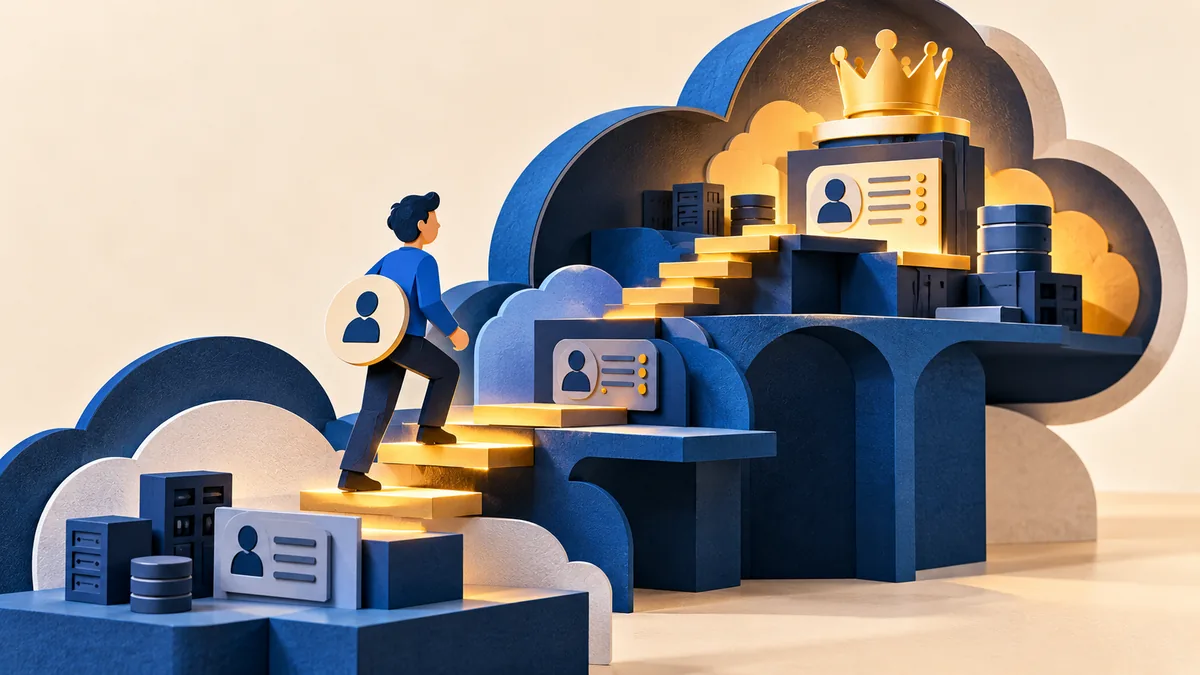
A cloud role can have more power than its name suggests. Identity and access management, often shortened to IAM, controls which people and services may perform cloud actions. A role with apparently limited permissions may still be able to change another identity or launch a more powerful service.
Understand the idea
Read permissions as a sequence of possible actions. Can this identity change a trusted role, attach a policy, or run a workload using another identity? Several small permissions can combine into a path to administrator access. Review the final authority the role can reach, not only the first permission listed.
- Identity
Record the principal and its effective permissions.
- Path
Trace actions that can change or assume greater authority.
- Boundary
Remove unnecessary paths and verify the remaining workflow.
A practical example
Imagine a reporting service that only needs to read a storage folder. It can also change the permissions of a role used by a deployment system. That extra permission creates a route far beyond reporting. The team removes it and confirms that scheduled reports still complete.
What to do next
- Prefer short-lived passwords and access keys. Use federation for people and workload roles for services where supported. Retire unnecessary static keys.
- Separate deployment from permission administration. Restrict which roles a pipeline can assign or pass, and which trust relationships it can modify.
- Apply guardrails at the appropriate scope. Use least-privilege policies, permission boundaries, or organization controls where they fit. These mechanisms have different semantics; test their combined effect.
- Review changes as security events. Alert on unexpected policy attachment, role trust changes, credential creation, and removal of important logging controls.
How to check the result
Record the task the role must perform and the access needed for it. After removing a permission, retest both the legitimate task and the unwanted route to greater authority.
The role is not called Administrator. Is it low risk?
The name is not evidence. A combination of permissions may enable privileged actions through another role or service. Assess effective authority and the intended task.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.