
Showing 1–5 of 5 articles
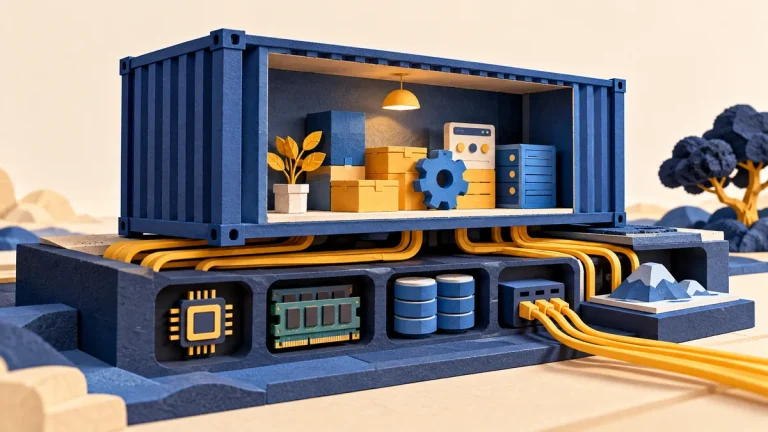
What a container does not isolate
A container’s boundary depends on its configuration and the host it shares. Review privilege, mounted resources, credentials, network access, and runtime controls as a complete deployment.
Read the visual guide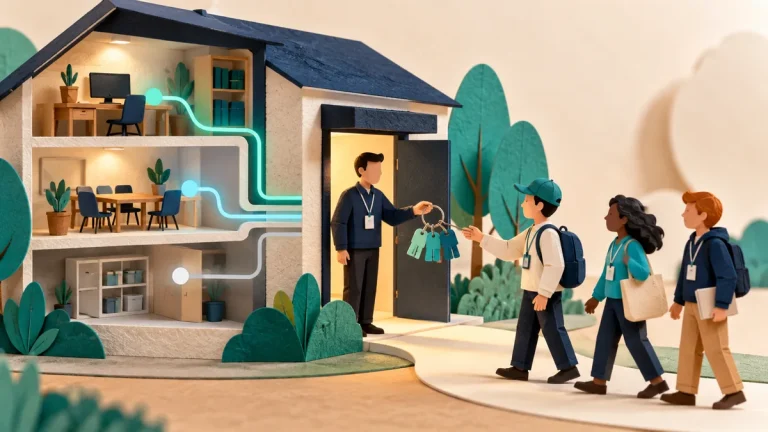
How a small organisation should give volunteers access
Volunteers need access that fits their actual work, including a clear owner and a defined review point. Shared accounts and indefinite permissions make changes harder to control.
Read the visual guide
Who should have administrator rights on a work laptop
Administrator access changes what software can do to a device. Limit routine privilege while giving staff a clear, workable route for approved installation and support.
Read the visual guide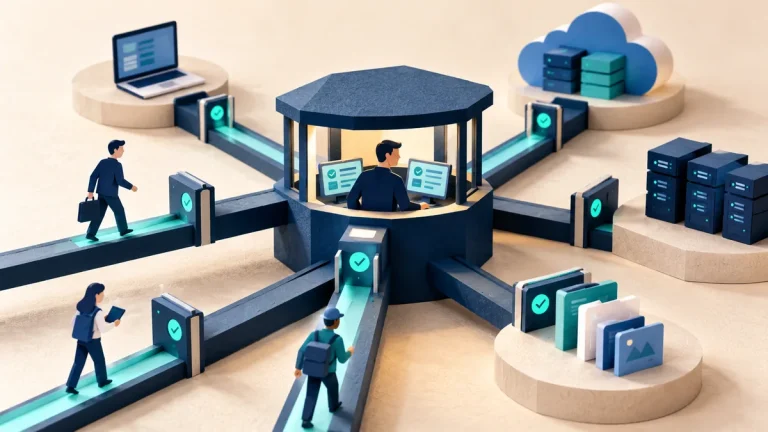
Practical zero trust: verify access to each important service
For a small team, zero trust starts with explicit access decisions around important services. Identity, device context, least privilege, and review matter more than adopting a label.
Read the visual guide
Cloud IAM escalation: when a small permission becomes admin access
A role can gain power indirectly by changing another identity, passing a privileged role, or altering a workload. Review what permissions make possible together, not only their individual names.
Read the visual guide