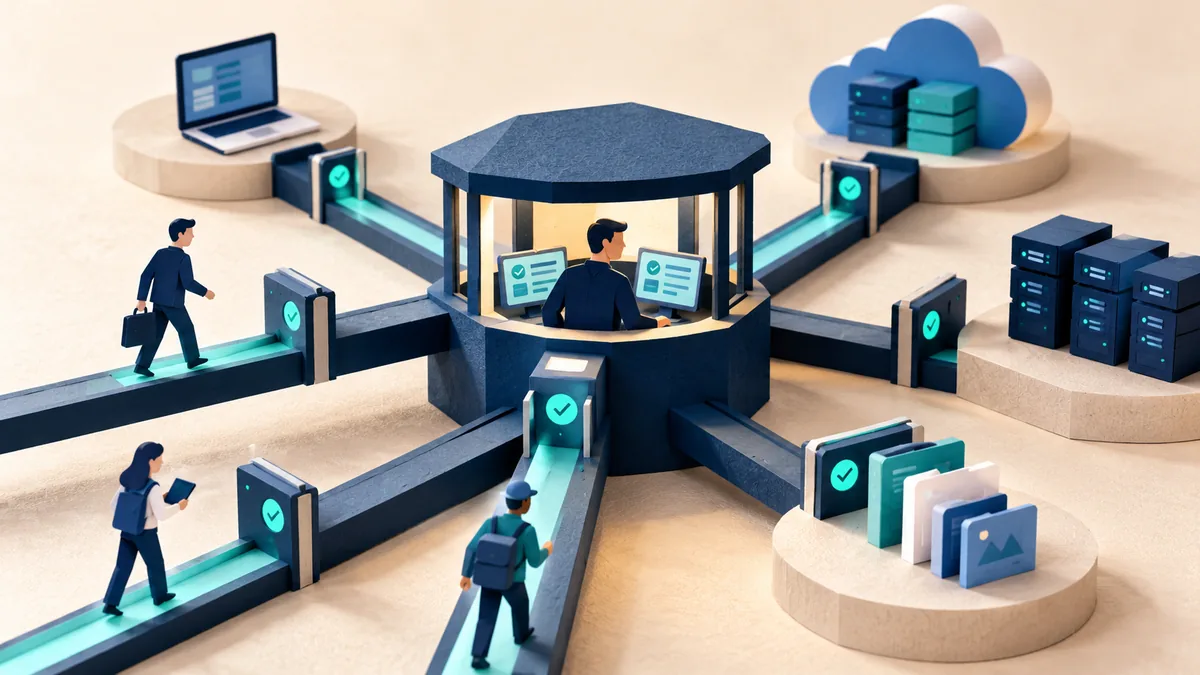
Zero trust is an approach to access decisions: being on an office network does not automatically make a request trustworthy. A person or device still needs appropriate identity and permission checks for the service it wants to use. For a small team, this starts with a manageable improvement to one important service.
Understand the idea
Choose a service and name its users, devices, sensitive actions, and recovery routes. Then decide which checks fit those actions. Strong sign-in, limited permissions, controlled administration, and useful records can each improve the boundary. Buying a product with a zero-trust label does not define those rules for you.
- Service
Choose a system and the work it supports.
- Decision
Define which identity may do what, from which context.
- Review
Remove exceptions that no longer serve a real task.
A practical example
Imagine a team protecting its cloud file store. Staff receive individual accounts, sensitive folders have named groups, administrators use stronger sign-in, and departing staff lose access promptly. The team tests an ordinary user’s access rather than relying only on a diagram.
What to do next
- Move the chosen service to named accounts and remove unnecessary shared access.
- Require appropriate MFA and test lost-factor recovery. Prefer phishing-resistant options where supported.
- Separate routine work from administration and restrict privileged access to the approved devices or management path.
- Review access when people join, change roles, and leave. Include connected applications and service identities.
- Collect sign-in and administrative-change events and assign someone to investigate exceptions.
How to check the result
Choose a clear before-and-after test for the service. The intended users should still work, while an unapproved user or device should not gain the same access merely by joining the network.
Do we need to replace everything at once?
Start with a bounded service and a specific access problem. Verify that the chosen controls work for staff and administrators before expanding the approach.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.