Ransomware can stop a team from using its files and systems. By the time encryption starts, an intruder may already have spent time inside the organization. Prevention therefore begins with the ways someone could first gain access, rather than with the encryption program alone.
Understand the idea
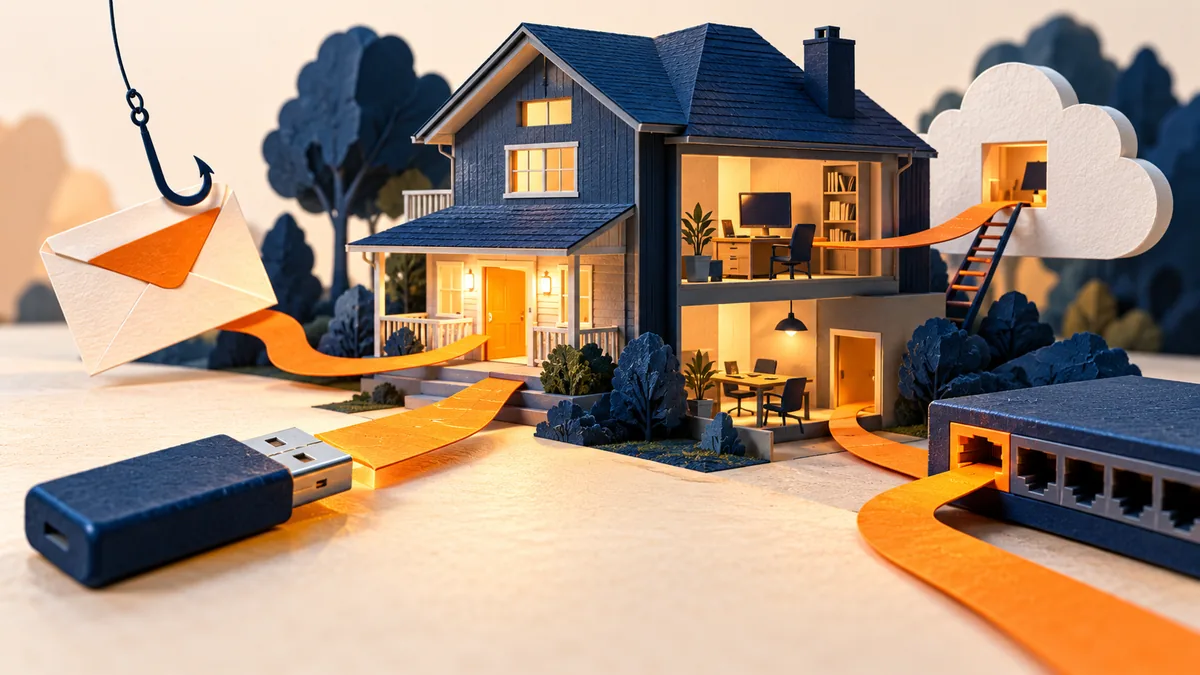
Common entry routes include stolen account details, exposed remote-access services, malicious messages, and software weaknesses. After getting in, an attacker may seek stronger permissions and backups. A useful review connects the entry route to the systems and information it could reach.
- Entry
Identify a reachable service, identity, or delivered file.
- Access
Look for the attacker’s ability to move or change systems.
- Resilience
Contain the route and verify recovery from protected copies.
A practical example
Imagine a small office restoring servers after a ransomware incident. If the exposed support account still works, the same access route may remain available. The recovery team checks that account, other affected identities, and the backup administration process before reconnecting restored systems.
What to do next
- Review the ways in. List remote-access services, public appliances, important accounts, and supplier tools. Check who owns each route and whether it is still needed.
- Close the relevant weaknesses. Apply supported updates, restrict unnecessary exposure, and strengthen sign-in for the accounts involved. Test normal work after the change.
- Prepare recovery separately. Check who can change or delete backups. Restore a sample into a safe environment and confirm that the people responsible can use it.
- Investigate active signs. If there are signs of intrusion, involve the response team. Preserve relevant records and assess continuing access and possible information exposure.
How to check the result
Record which access route was closed, how that was tested, and whether recovery copies were restored successfully. Recovery also needs a decision about possible information exposure; working files do not settle that question.
We have backups. Do we still need to investigate the entry point?
Yes. Restoring systems without addressing access can leave the same route available. Recovery also needs evidence about affected identities, persistence, and possible data exposure.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.