
Showing 1–6 of 6 articles
How to run vulnerability management as a queue
A vulnerability queue needs clear ownership, prioritization, and a way to establish closure. Ticket counts matter less than whether important exposure is actually reduced.
Read the visual guide
What to do with a software bill of materials
A software bill of materials lists components in a product or release. Its value comes from matching that inventory to deployed systems, relevant advisories, owners, and update decisions.
Read the visual guide
How a team of five can patch without stopping the work
A workable patch routine names an owner, prioritizes exposed and important systems, and checks the affected workflow after an update. Keep exceptions visible rather than indefinitely postponed.
Read the visual guide
How to install the real software update and ignore the fake one
An update prompt should lead back to the software’s established update mechanism or official publisher. A web advertisement claiming an urgent update is a different starting point.
Read the visual guide
Plugin and package risk: check the dependency you actually deploy
A useful dependency brings another project’s code into your environment. Review its source, maintenance, permissions, version, and update path before making it part of a critical service.
Read the visual guide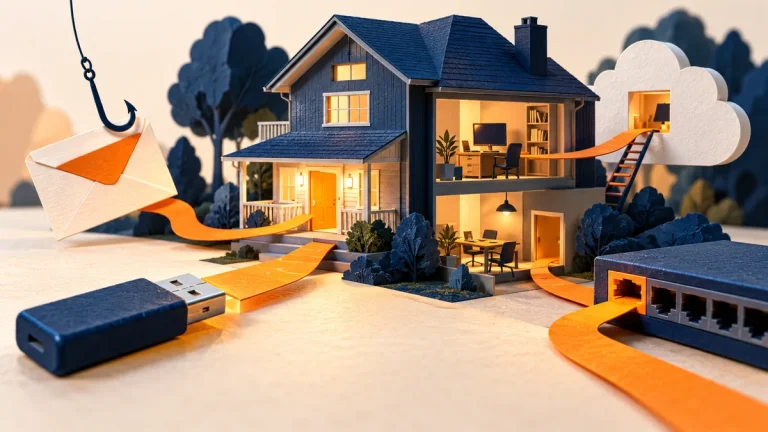
Ransomware entry points: close access before encryption begins
Ransomware response starts before files are encrypted. Compromised identities, exposed remote services, malicious messages, and vulnerable software can each provide an entry path.
Read the visual guide