
Showing 37–39 of 39 articles
Page 4 of 4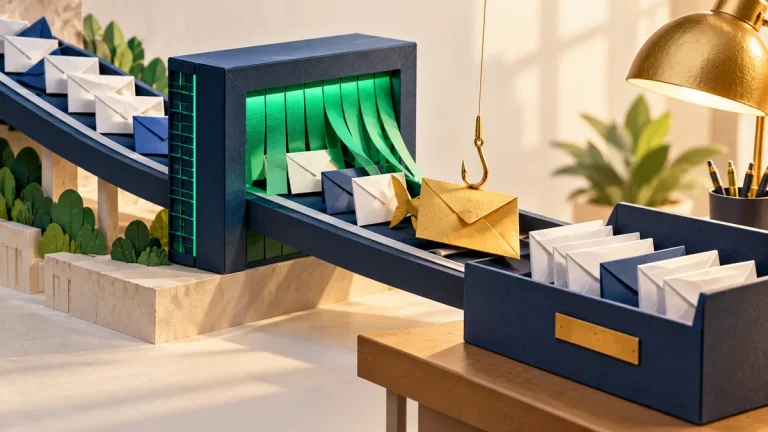
Phishing beyond the email filter: verify the request, not the badge
An email that passes technical checks can still ask you to do something harmful. A trusted sender’s account may be compromised, and a plausible message may lead to an unsafe action.
Read the visual guide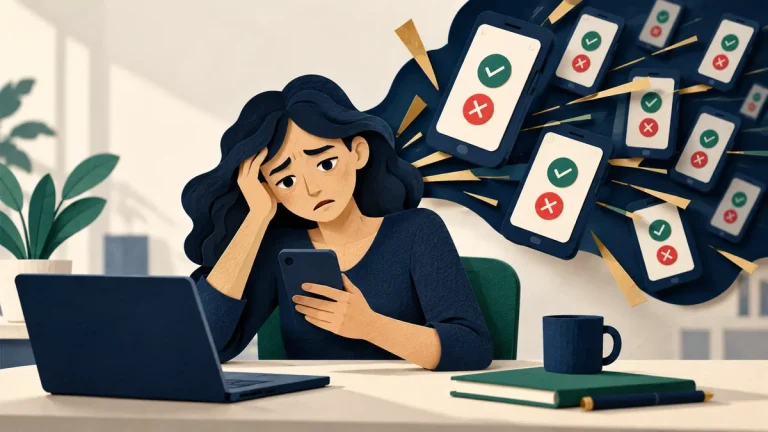
MFA push fatigue: what to do with unexpected approval requests
Repeated sign-in prompts can pressure someone into approving access they did not start. Treat an unexpected approval request as a signal to stop, verify, and investigate.
Read the visual guide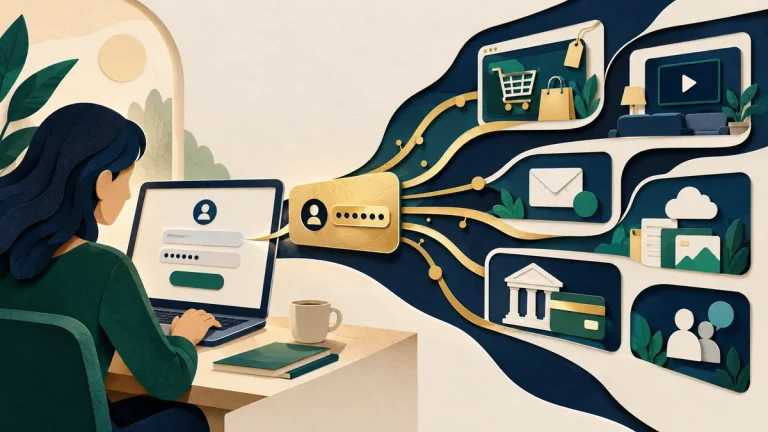
Stolen passwords: stop credential stuffing across every login route
An attacker can reuse a stolen password through more than the main sign-in page. Review mobile APIs, legacy access, and recovery routes alongside the login form.
Read the visual guide