
Showing 1–2 of 2 articles
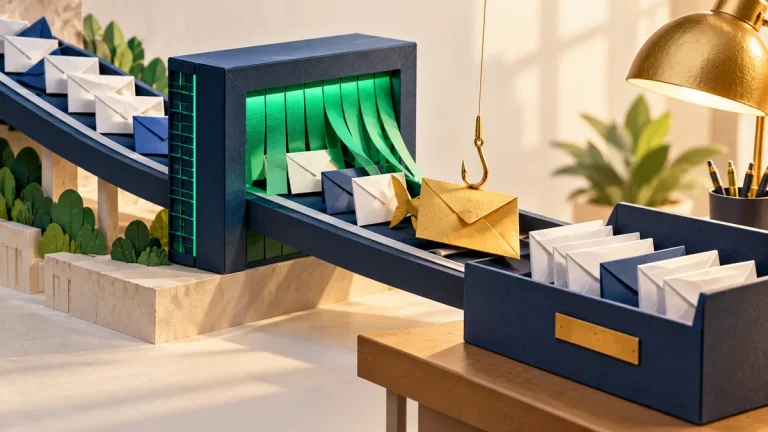
Phishing beyond the email filter: verify the request, not the badge
An email that passes technical checks can still ask you to do something harmful. A trusted sender’s account may be compromised, and a plausible message may lead to an unsafe action.
Read the visual guide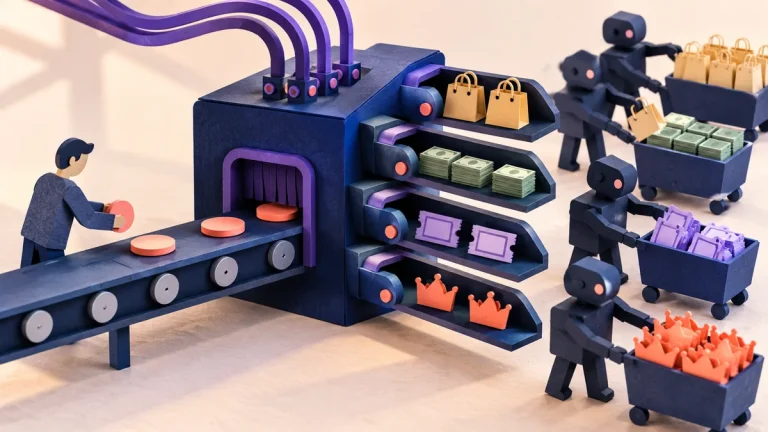
API business-logic abuse: valid requests can still cause harm
An API request can be correctly formatted and still misuse a workflow. Review the business outcome, especially repeated actions, ownership checks, and limits that span several requests.
Read the visual guide