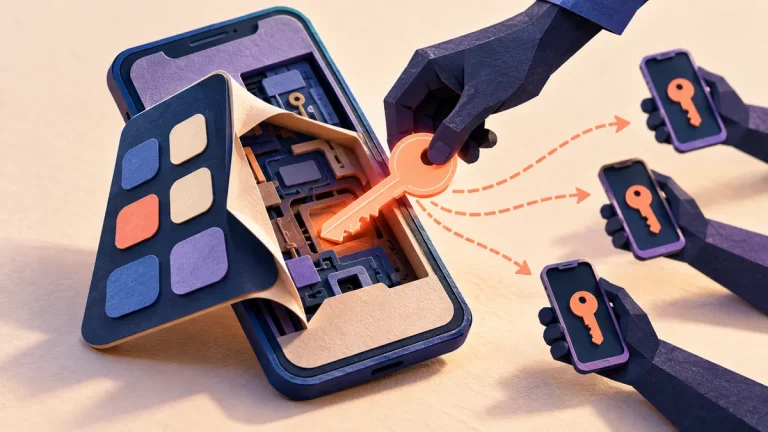
Do not put a secret API key inside a mobile app
An application you distribute to users cannot reliably hide a shared secret embedded in its code or resources. Put privileged authorization behind an appropriate server-side boundary.
Read the visual guide