
Showing 1–4 of 4 articles
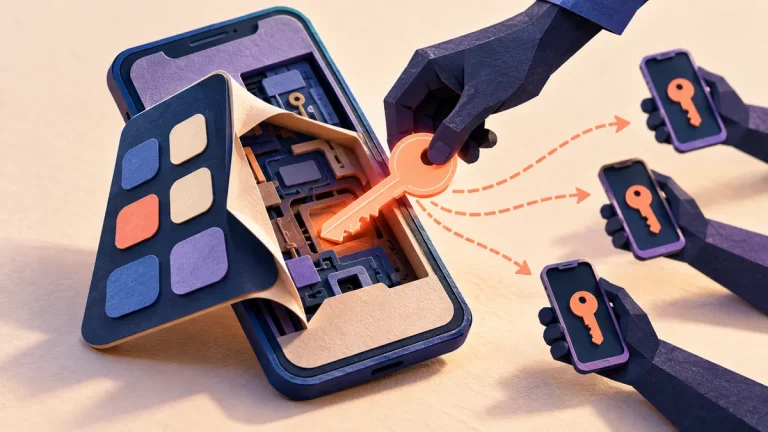
Do not put a secret API key inside a mobile app
An application you distribute to users cannot reliably hide a shared secret embedded in its code or resources. Put privileged authorization behind an appropriate server-side boundary.
Read the visual guide
Passwords that are still in Git history
Deleting a secret from the latest version does not invalidate it or remove every earlier copy. Contain the credential first, then assess repository history and any evidence of use.
Read the visual guide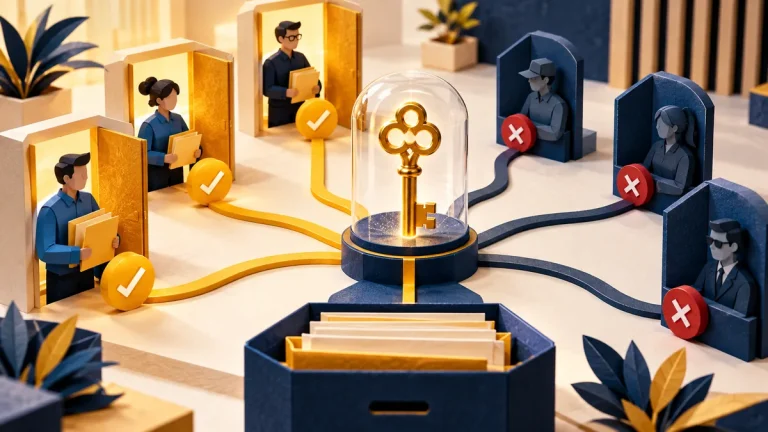
Who can use an encryption key, and how you would know
The right to manage a key and the right to use it are different powers. Review who can decrypt, change policy, rotate, export, or delete keys, and what evidence those actions leave.
Read the visual guide
What to do when a password is pasted into chat
Deleting a chat message does not invalidate a password or token that someone may have copied. Identify the credential, revoke or rotate it, and review its possible use.
Read the visual guide