
Showing 1–4 of 4 articles
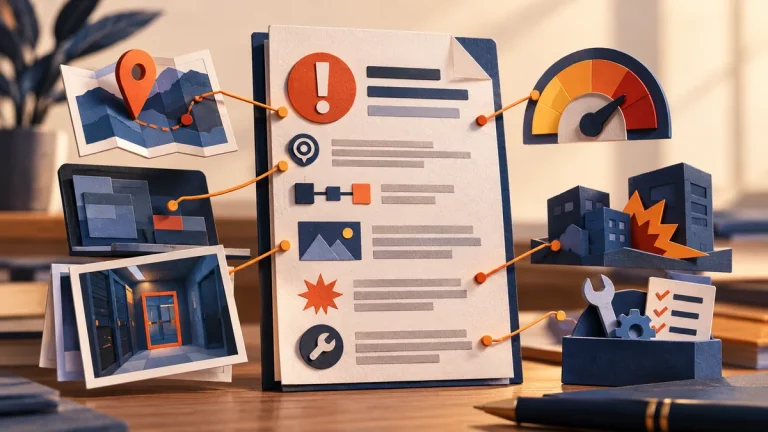
What a security finding should contain
A useful finding gives its owner enough information to understand and verify the problem. Identify the affected asset, safe evidence, practical consequence, and a correction with a clear completion test.
Read the visual guide
How to run vulnerability management as a queue
A vulnerability queue needs clear ownership, prioritization, and a way to establish closure. Ticket counts matter less than whether important exposure is actually reduced.
Read the visual guide
What to do with a software bill of materials
A software bill of materials lists components in a product or release. Its value comes from matching that inventory to deployed systems, relevant advisories, owners, and update decisions.
Read the visual guide
An open-source licence is not a security review
Being able to inspect source code is valuable, but it does not prove that a component has been reviewed or is safe for your use. Assess the actual dependency and its operating context.
Read the visual guide