
Showing 1–3 of 3 articles
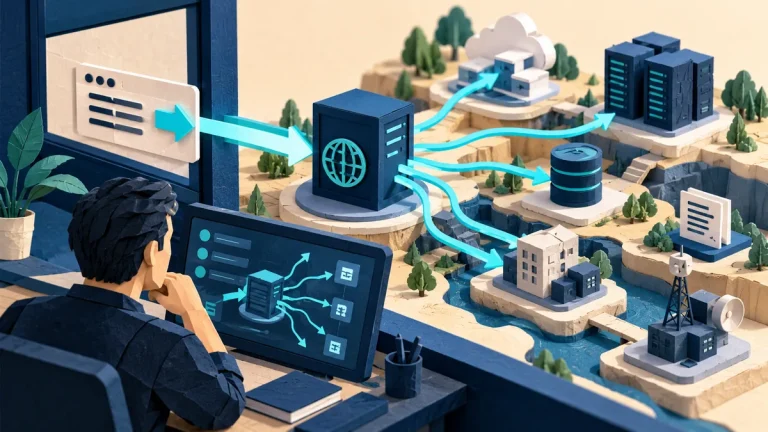
SSRF explained: when a server fetches a destination it should not
A server-side request feature can reach resources that the user cannot directly access. Review allowed destinations and the authority available to the fetching service.
Read the visual guide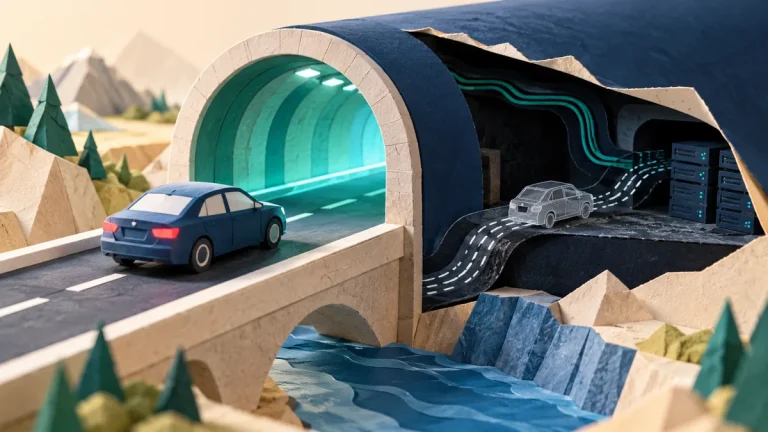
TLS checks: protect the connection all the way to the service
A valid certificate at the public edge is only part of a secure connection. Review protocol settings, hostname validation, internal hops, and the origin that ultimately handles the request.
Read the visual guide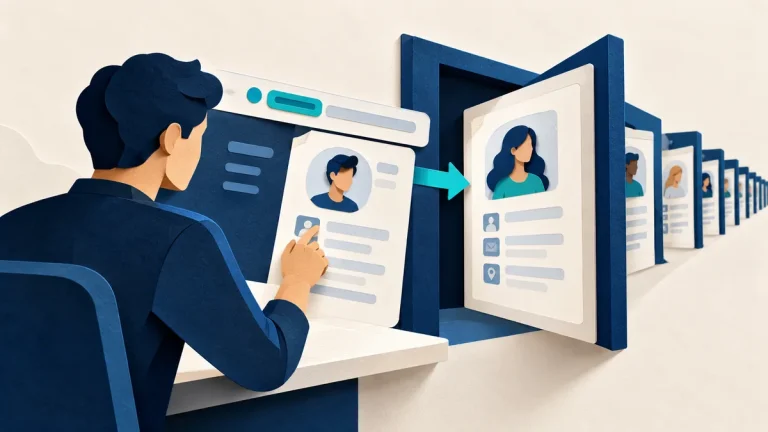
Broken access control: can one user reach another user’s data?
Being signed in should not give a person access to every record. The server must check permission for the specific object and action on every request.
Read the visual guide