
Showing 1–8 of 8 articles
Staging sites that are still open on the internet
A staging site can contain production data and powerful integration credentials. Keep its access and outbound behavior deliberately separate from the live service.
Read the visual guide
How to handle a security report from someone you do not know
A report from an unfamiliar person may identify a real issue. Provide a controlled route to receive it, assess the evidence, and decide the next step without encouraging unnecessary testing.
Read the visual guide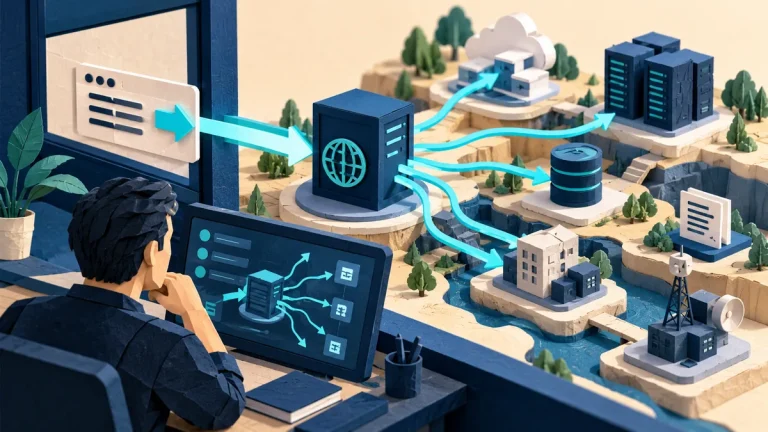
SSRF explained: when a server fetches a destination it should not
A server-side request feature can reach resources that the user cannot directly access. Review allowed destinations and the authority available to the fetching service.
Read the visual guide
DDoS attacks: distinguish bandwidth floods from application overload
A service can fail because the network link is saturated or because expensive application requests consume its resources. The appropriate mitigation depends on where capacity is exhausted.
Read the visual guide
Web shells: remove the attacker’s access, not just one file
An unexpected server-side script may provide an attacker with continuing access. Removing that file is only one step; you also need to understand how it arrived and what else changed.
Read the visual guide
TLS checks: protect the connection all the way to the service
A valid certificate at the public edge is only part of a secure connection. Review protocol settings, hostname validation, internal hops, and the origin that ultimately handles the request.
Read the visual guide
Broken access control: can one user reach another user’s data?
Being signed in should not give a person access to every record. The server must check permission for the specific object and action on every request.
Read the visual guide
Website scanning bots: is it probing or a real breach?
A scan in your logs shows that someone asked a question. The response—and what happened next—tells you whether they reached something valuable. Start there before declaring a breach.
Read the visual guide