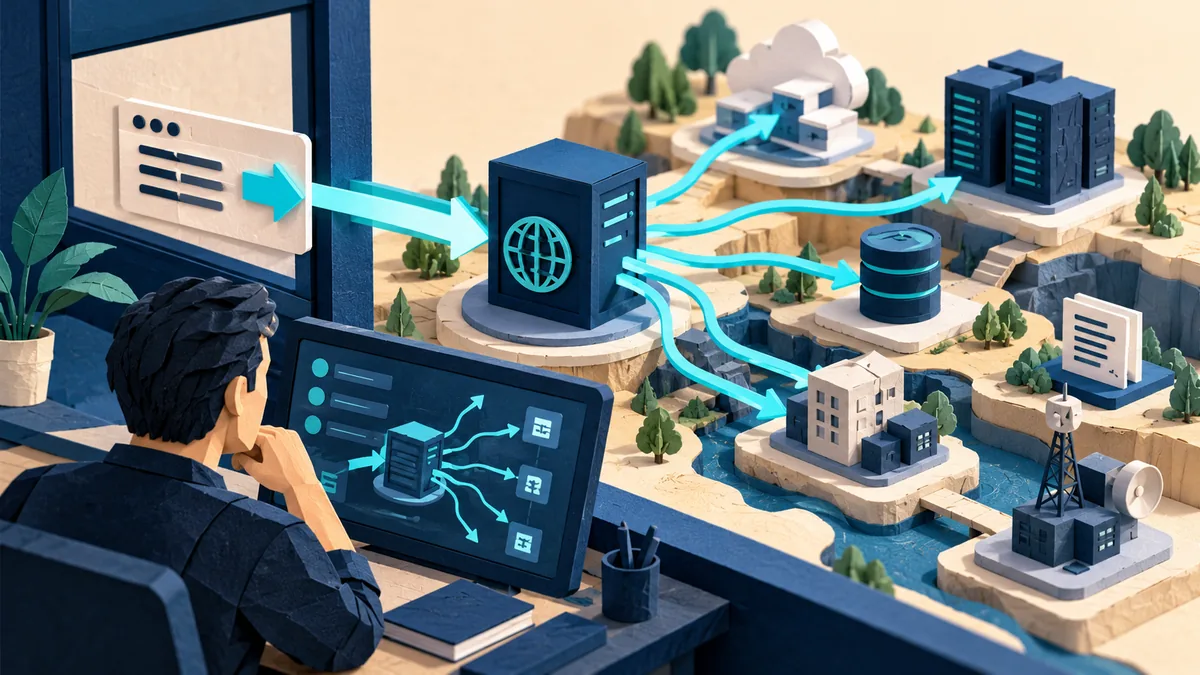
Some applications fetch a URL on a user’s behalf, such as when importing an image or previewing a link. Server-side request forgery, or SSRF, occurs when that feature lets someone make the server contact a destination it should not reach. The server may have access that the user does not.
Understand the idea
Review what the feature actually needs to contact. A public image importer usually does not need access to internal management services. Define permitted destinations and protocols, then control network access as another layer. Check redirects and address resolution too, because the final destination can differ from the original text.
- Input
A user influences a destination or remote resource.
- Fetch
The server makes the request using its own network access.
- Boundary
Restrict destinations, redirects, and backend reachability.
A practical example
For example, a support portal imports images for tickets. The team restricts the feature to approved storage locations and tests the expected imports. It also checks that the import service cannot reach private administration endpoints that have nothing to do with ticket images.
What to do next
- Restrict the feature. Prefer identifiers for approved resources over arbitrary URLs where the product can support that design.
- Separate the fetching service. Run it with limited network access and no unnecessary passwords and access keys. Restrict access to internal and metadata services through appropriate platform controls.
- Constrain the request. Limit protocols, response size, timeouts, redirects, and resource consumption. Do not forward a user's unrelated authorization headers or internal service passwords and access keys.
- Log decisions safely. Record destination category, outcome, and correlation details without exposing secrets embedded in URLs.
How to check the result
Use controlled destinations in an approved environment to test the boundary. Record both successful legitimate imports and refused destinations, including redirect behavior.
We block one internal address. Is the fetcher isolated?
Review the complete destination-validation and network boundary, including redirects and resolved addresses. Test only within an approved scope and keep sensitive internal services unreachable.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.