
Showing 1–8 of 8 articles
Re-check a payment limit at the moment you pay
A limit checked before a payment can become stale while other requests are processed. Enforce the business rule at the transaction boundary, including concurrent actions and retries.
Read the visual guide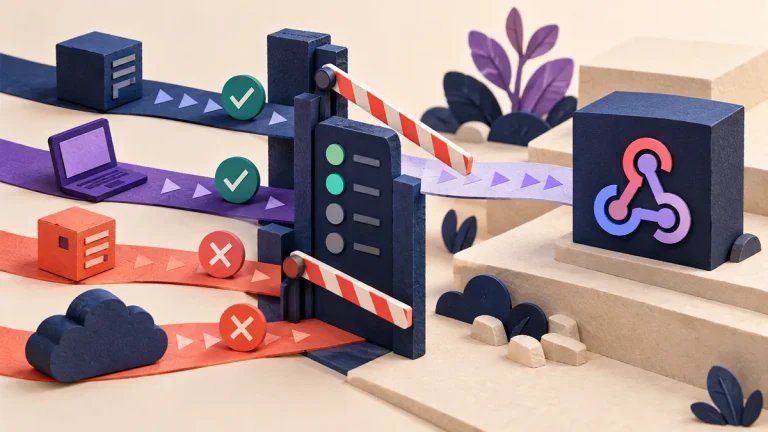
Check who is allowed to call your webhook
A webhook’s payload and familiar endpoint name do not prove who sent it. Validate the sender using its supported scheme, handle retries deliberately, and authorize the resulting business action.
Read the visual guide
Do not put a secret API key inside a mobile app
An application you distribute to users cannot reliably hide a shared secret embedded in its code or resources. Put privileged authorization behind an appropriate server-side boundary.
Read the visual guide
When your system acts with the wrong person’s authority
A service may have more access than the person asking it to act. It must check the caller’s authority before using its own powerful identity on that person’s behalf.
Read the visual guide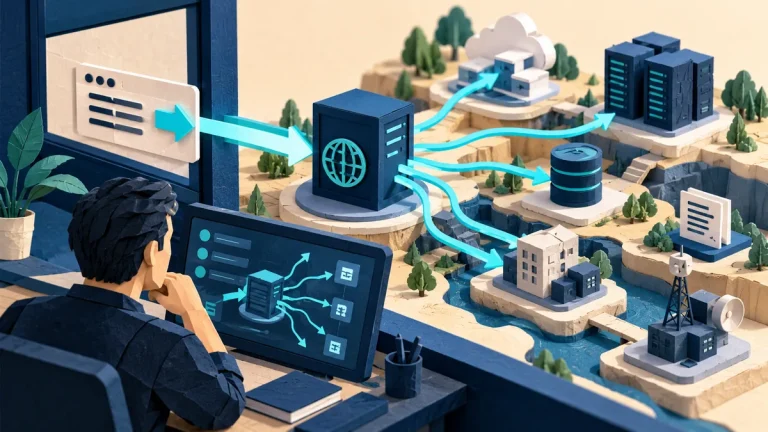
SSRF explained: when a server fetches a destination it should not
A server-side request feature can reach resources that the user cannot directly access. Review allowed destinations and the authority available to the fetching service.
Read the visual guide
API business-logic abuse: valid requests can still cause harm
An API request can be correctly formatted and still misuse a workflow. Review the business outcome, especially repeated actions, ownership checks, and limits that span several requests.
Read the visual guide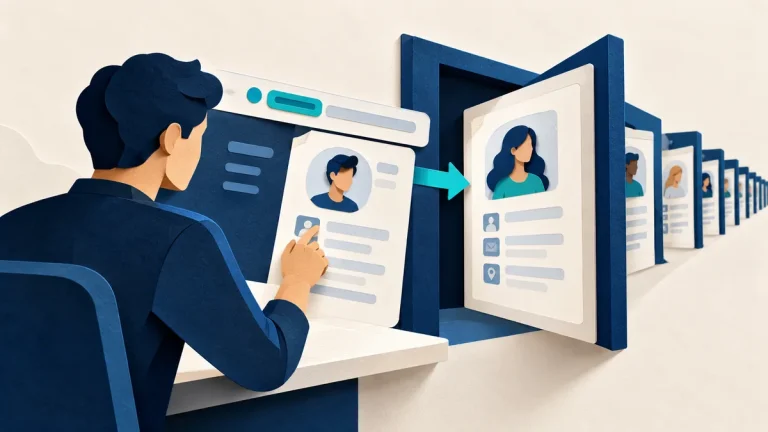
Broken access control: can one user reach another user’s data?
Being signed in should not give a person access to every record. The server must check permission for the specific object and action on every request.
Read the visual guide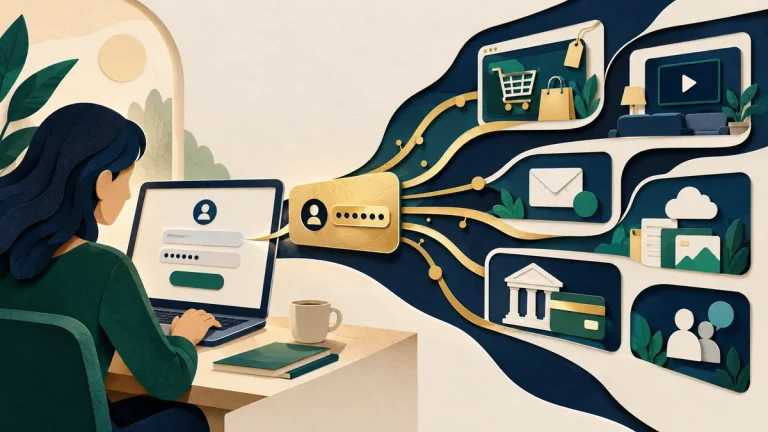
Stolen passwords: stop credential stuffing across every login route
An attacker can reuse a stolen password through more than the main sign-in page. Review mobile APIs, legacy access, and recovery routes alongside the login form.
Read the visual guide