
Showing 1–5 of 5 articles
Plugin and package risk: check the dependency you actually deploy
A useful dependency brings another project’s code into your environment. Review its source, maintenance, permissions, version, and update path before making it part of a critical service.
Read the visual guide
DDoS attacks: distinguish bandwidth floods from application overload
A service can fail because the network link is saturated or because expensive application requests consume its resources. The appropriate mitigation depends on where capacity is exhausted.
Read the visual guide
Ransomware entry points: close access before encryption begins
Ransomware response starts before files are encrypted. Compromised identities, exposed remote services, malicious messages, and vulnerable software can each provide an entry path.
Read the visual guide
Phishing beyond the email filter: verify the request, not the badge
An email that passes technical checks can still ask you to do something harmful. A trusted sender’s account may be compromised, and a plausible message may lead to an unsafe action.
Read the visual guide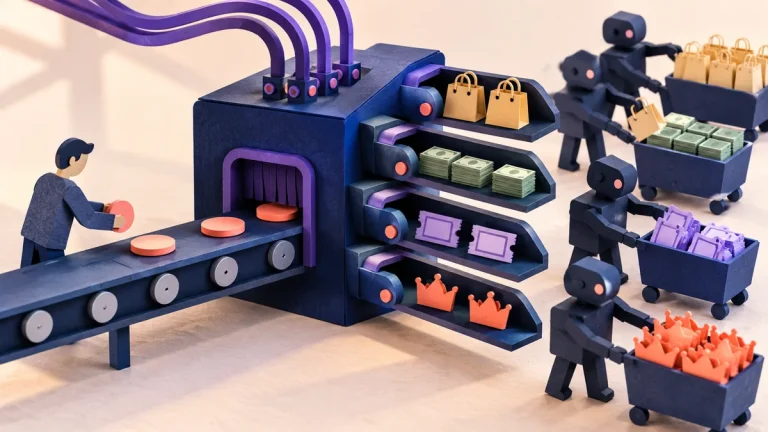
API business-logic abuse: valid requests can still cause harm
An API request can be correctly formatted and still misuse a workflow. Review the business outcome, especially repeated actions, ownership checks, and limits that span several requests.
Read the visual guide