
Showing 1–2 of 2 articles
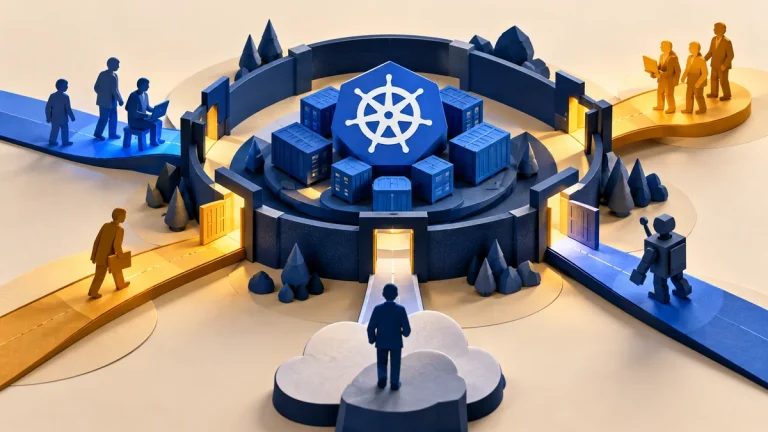
Who can reach a Kubernetes cluster
A cluster’s exposure includes more than its public endpoint. Review administrators, workload identities, role bindings, credentials, network paths, and access to sensitive configuration.
Read the visual guide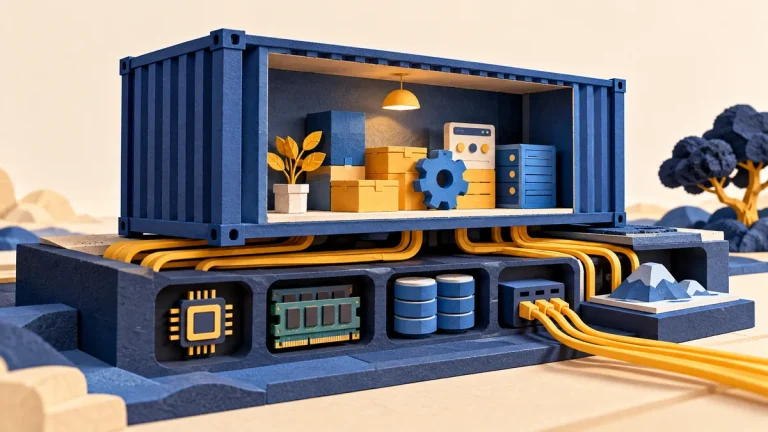
What a container does not isolate
A container’s boundary depends on its configuration and the host it shares. Review privilege, mounted resources, credentials, network access, and runtime controls as a complete deployment.
Read the visual guide