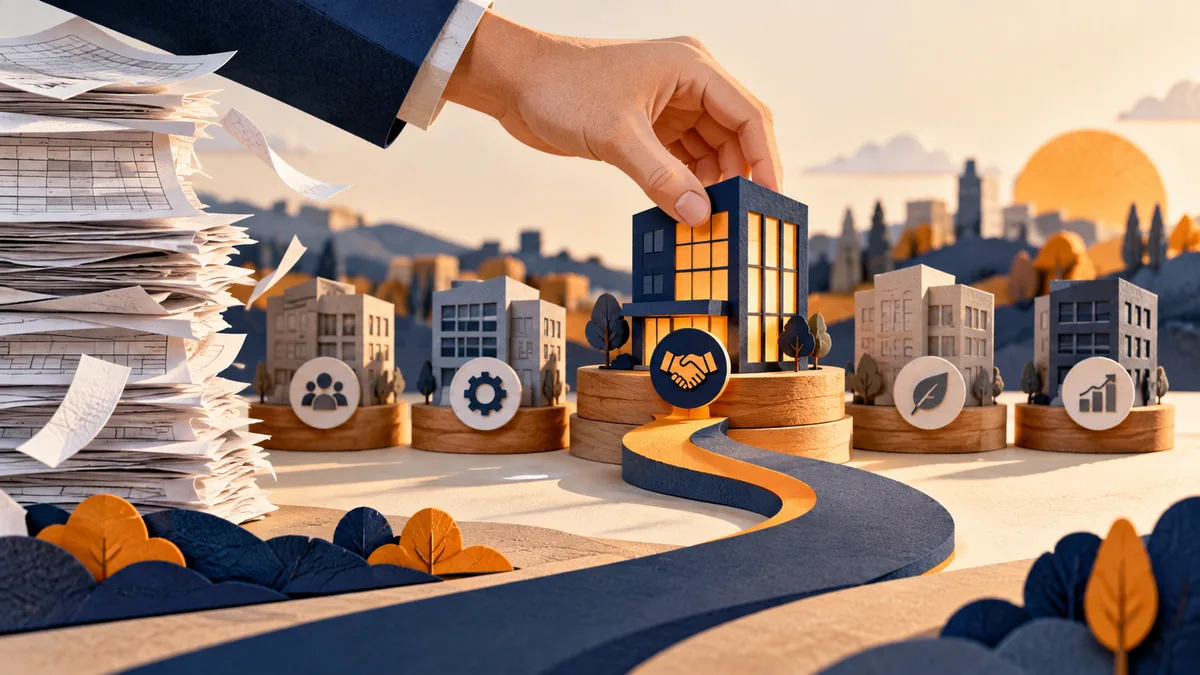
A supplier review should help you decide whether a service fits the information and access you plan to give it. A long questionnaire is not automatically a better review. Start with the supplier’s actual role and the consequence if it fails or mishandles the work.
Understand the idea
Ask what data the supplier receives, which systems it can access, how important the service is, and how you would leave or recover. Request evidence suited to those questions. A certificate or policy can support the review, but its scope and relevance need checking.
- Scope
Identify the service, data, access, and dependencies.
- Assurance
Ask for evidence proportionate to that scope.
- Decision
Record ownership, conditions, and a review point.
A practical example
Imagine an NGO comparing a public newsletter service with a provider handling sensitive case records. The second relationship needs closer attention to access, sharing, recovery, and contract terms. The review effort follows the responsibility rather than using the same large form for every purchase.
What to do next
- Access: Who receives administrative or data access, and how is it approved, protected, and revoked?
- Information: Where is the data handled, which other providers are involved, and how is retention or return managed?
- Recovery: What continuity and restoration arrangements are relevant, and what has actually been tested?
- Incidents: How will the supplier notify you and cooperate with investigation and evidence preservation?
- Exit: Can you retrieve required records and close access without depending on a departing individual?
How to check the result
Record the decision, evidence, remaining concerns, and owner. Review again when access, information, service importance, or the supplier’s arrangements change.
The supplier handles no customer records. Is the risk minimal?
Check administrative access, integrations, and operational dependency. A low-data service can still change a system or interrupt essential work.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.