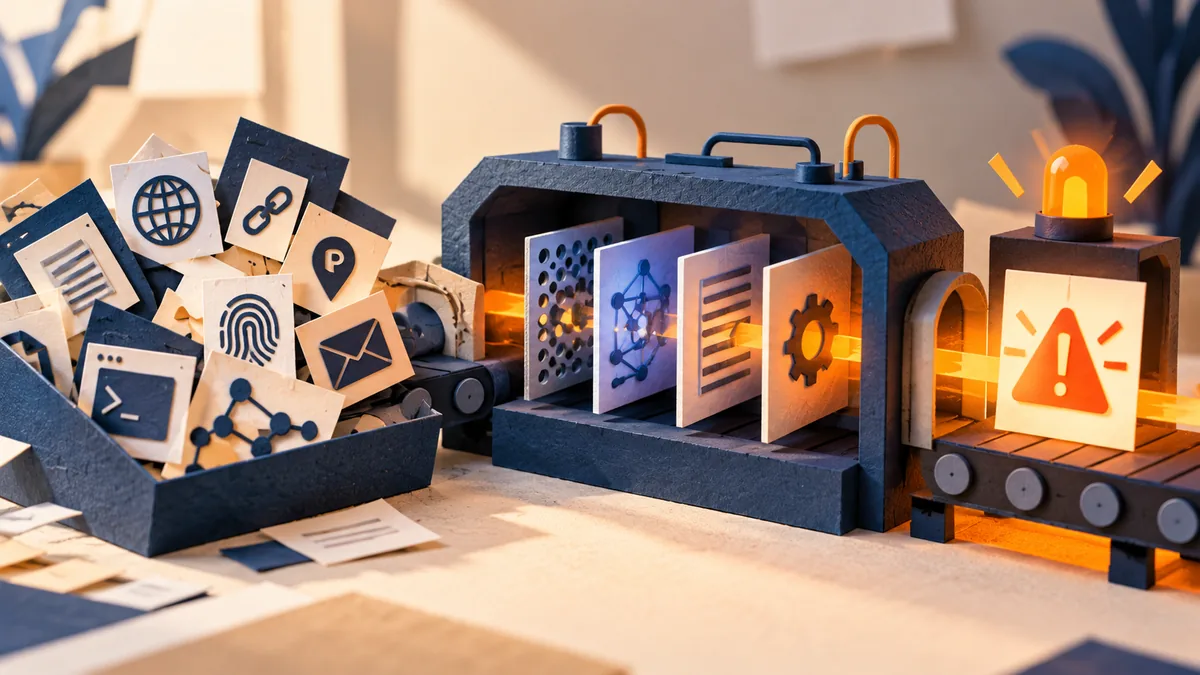
A security alert should help someone make a decision. Detection engineering is the work of turning a suspicious pattern into a tested alert, with the records and response steps needed to use it. A rule that fires is only the beginning; someone must understand what to check next.
Understand the idea
Write the detection as a question about activity. For example, did a normal user account change a sensitive administrator setting? Identify the data needed, the expected trigger, likely innocent explanations, and the person responsible for reviewing it. This keeps the rule connected to a useful action.
- Behavior
Describe the activity and why it matters.
- Signal
Confirm your records can reveal that behavior.
- Response
Test the alert and the person’s next action.
A practical example
Imagine a rule that alerts on every new administrator. A planned account setup creates many expected alerts. The team adds the approved-change context and a clear review step, while testing that an unapproved administrator change still reaches the responder.
What to do next
- Verify collection. Produce a harmless test event and find it in the actual data source. A connector marked “healthy” does not guarantee the needed fields arrive.
- Implement the rule. Document the assumptions, time window, exclusions, and conditions that distinguish an actionable event.
- Test positive and negative cases. Confirm that the intended behavior alerts and that ordinary approved activity does not create unmanageable noise.
- Test delivery and response. The alert must reach an available person with enough context and a runbook they can follow.
- Review outcomes. Record false positives, missed cases, investigation time, and changes made after tuning.
How to check the result
Keep the test event, rule version, result, and response owner. Repeat the test when a data source or application changes; a quiet alert queue can also mean the detection stopped working.
The rule fired in a test. Is the detection ready?
Check that the right team received useful context and knew what to do. Also test expected benign behavior so alert volume remains manageable.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.