
Showing 1–10 of 10 articles
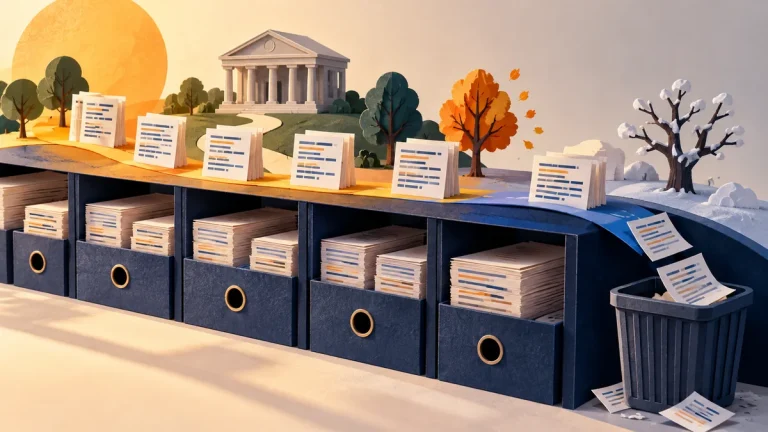
How long to keep security logs
Retention is an operational decision about which events must remain available, for how long, and at what cost and sensitivity. Connect the window to incident questions and real search capability.
Read the visual guide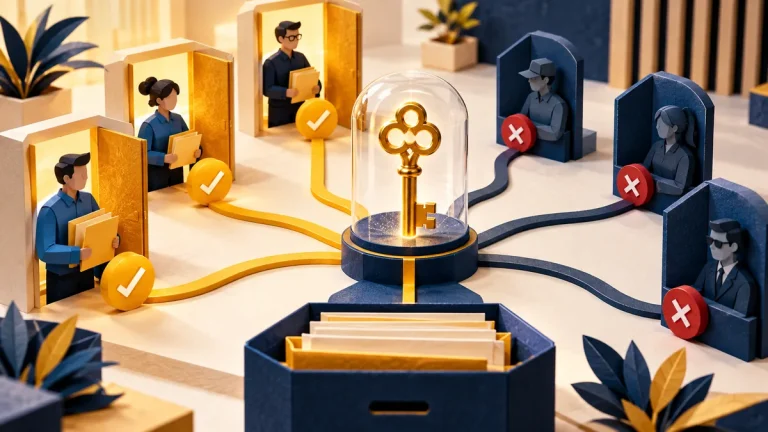
Who can use an encryption key, and how you would know
The right to manage a key and the right to use it are different powers. Review who can decrypt, change policy, rotate, export, or delete keys, and what evidence those actions leave.
Read the visual guide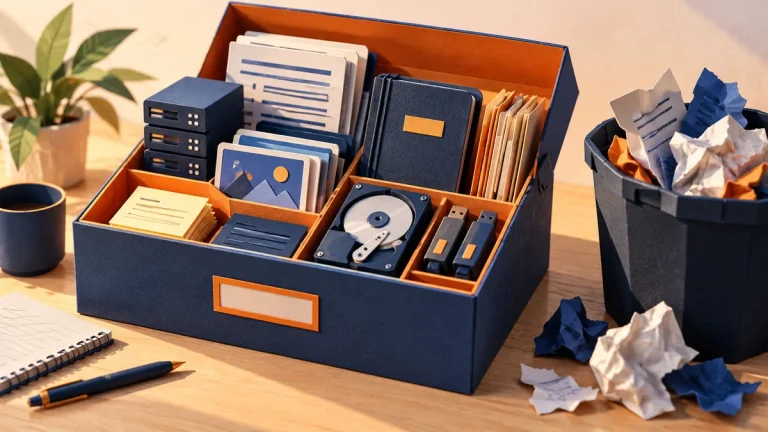
What to keep after a security incident
Useful evidence includes the original record, its source, the collection method, and the limits of what it shows. Keep investigation copies separate from originals and control access to both.
Read the visual guide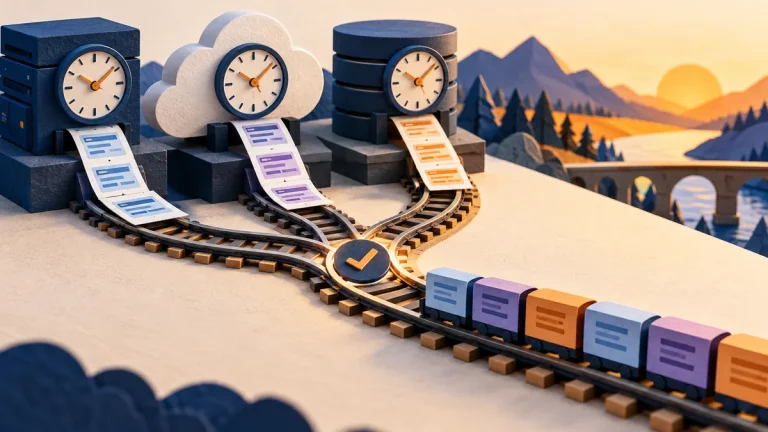
Why log times have to agree before you can trust the order
The order shown by two log systems may reflect clock settings, time zones, or ingestion delay rather than the true event sequence. Preserve those distinctions while building a timeline.
Read the visual guide
What to decide before you buy a security monitoring tool
A monitoring product creates value only when the right data reaches it and someone can act on its findings. Start with concrete detection stories and a bounded pilot.
Read the visual guide
Brute force or password spraying? Read the sign-in pattern
Repeated guesses against one account and a few guesses across many accounts create different patterns. Review events across identities and time, rather than looking only for one noisy username.
Read the visual guide
Detection engineering: turn a threat idea into an actionable alert
An alert needs more than a matching indicator. Connect the behavior you want to detect to available telemetry, a tested rule, an owner, and a clear response.
Read the visual guide
Incident logs: collect the evidence that answers your questions
A useful log source answers a specific incident question. Start with identities, affected services, and the actions you need to reconstruct, then preserve the records with their time context.
Read the visual guide
Living-off-the-land activity: spot misuse of legitimate tools
A familiar administration tool can be part of an intrusion. Judge its execution by the account, parent process, command context, destination, and business reason.
Read the visual guide
Website scanning bots: is it probing or a real breach?
A scan in your logs shows that someone asked a question. The response—and what happened next—tells you whether they reached something valuable. Start there before declaring a breach.
Read the visual guide