What to put in an evidence pack for a lawyer
An evidence pack should let an authorized legal reviewer understand the sources, timeline, handling, and gaps. Ask counsel to direct legal scope and distribution while keeping the technical record clear.

Incident Analysis
An evidence pack should let an authorized legal reviewer understand the sources, timeline, handling, and gaps. Ask counsel to direct legal scope and distribution while keeping the technical record clear.
People can make better decisions when an incident update identifies facts, gaps, current actions, and the next communication point. Avoid letting a confident tone outrun the evidence.
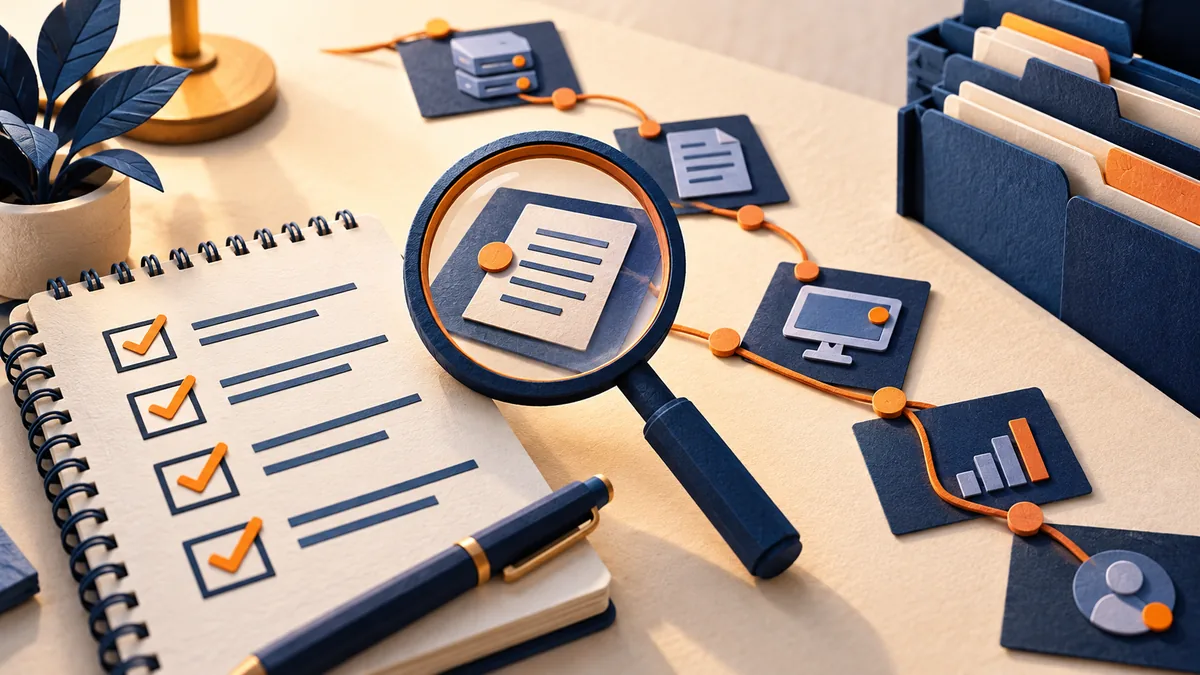
A defensible detection record connects the rule, its data, a test, an event, and the action taken. Keep that chain readable without requiring someone to reconstruct it from unrelated screenshots.
Useful evidence includes the original record, its source, the collection method, and the limits of what it shows. Keep investigation copies separate from originals and control access to both.
The order shown by two log systems may reflect clock settings, time zones, or ingestion delay rather than the true event sequence. Preserve those distinctions while building a timeline.
A useful log source answers a specific incident question. Start with identities, affected services, and the actions you need to reconstruct, then preserve the records with their time context.
A familiar administration tool can be part of an intrusion. Judge its execution by the account, parent process, command context, destination, and business reason.
An unexpected server-side script may provide an attacker with continuing access. Removing that file is only one step; you also need to understand how it arrived and what else changed.