
Showing 13–21 of 21 articles
Page 2 of 2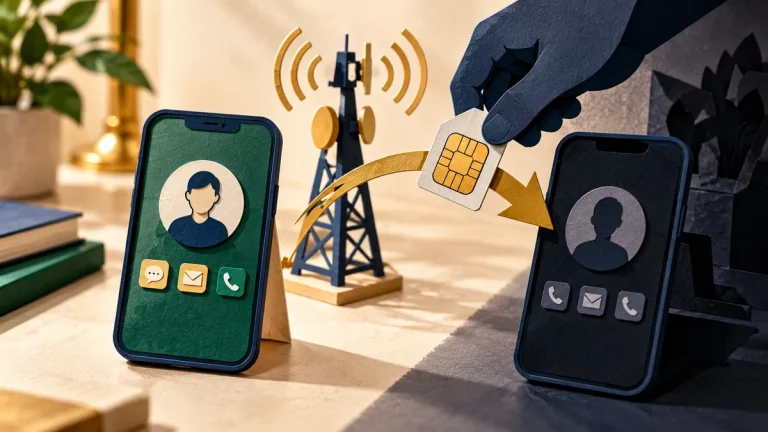
What a SIM swap is, and how to make one harder
If someone takes control of your mobile number, messages and calls intended for you may reach them. Protect the carrier account and review which services rely on that number for recovery.
Read the visual guide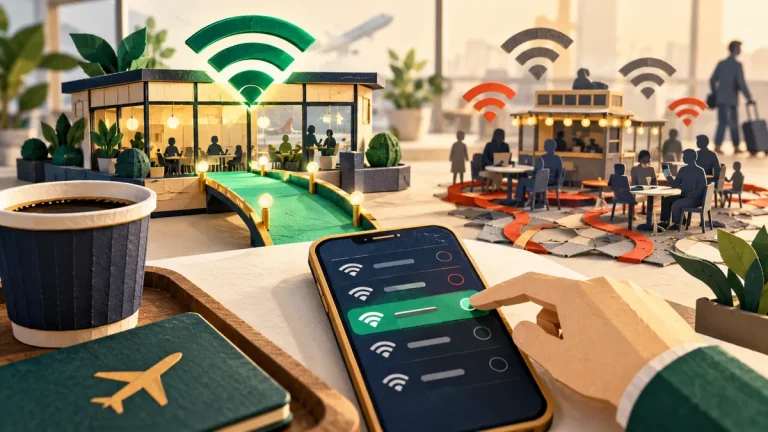
How to use public Wi-Fi without guessing
A familiar-looking network name does not prove who runs it. Confirm the network with the venue, keep device sharing controlled, and use your usual secure services.
Read the visual guide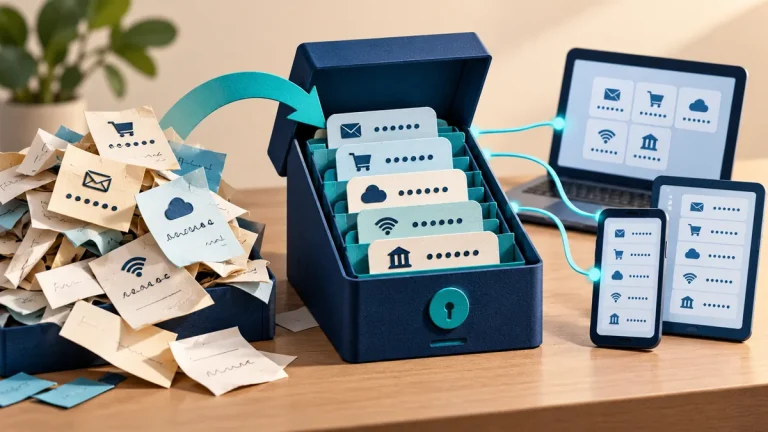
How to start using a password manager
A password manager helps you use a different strong password for each service. The first task is protecting the vault and making sure you can recover access to it.
Read the visual guide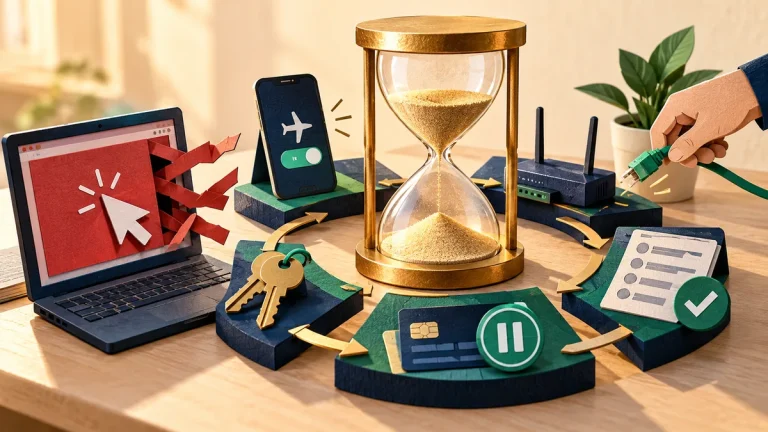
What to do in the first hour after you click a bad link
What happened after the click matters. Simply opening a page, entering a password, approving a request, and running a file call for different responses.
Read the visual guide
What to do when a text says it is from your bank
A message that looks like it came from your bank may be trying to lead you elsewhere. Open the bank’s usual app or use a number you already trust to check the claim.
Read the visual guide
Brute force or password spraying? Read the sign-in pattern
Repeated guesses against one account and a few guesses across many accounts create different patterns. Review events across identities and time, rather than looking only for one noisy username.
Read the visual guide
Stolen session cookies: why a password reset may not end access
A session cookie can let a browser continue using an account after sign-in. If a session is stolen, changing the password may not revoke every active session or connected application.
Read the visual guide
MFA push fatigue: what to do with unexpected approval requests
Repeated sign-in prompts can pressure someone into approving access they did not start. Treat an unexpected approval request as a signal to stop, verify, and investigate.
Read the visual guide
Stolen passwords: stop credential stuffing across every login route
An attacker can reuse a stolen password through more than the main sign-in page. Review mobile APIs, legacy access, and recovery routes alongside the login form.
Read the visual guide