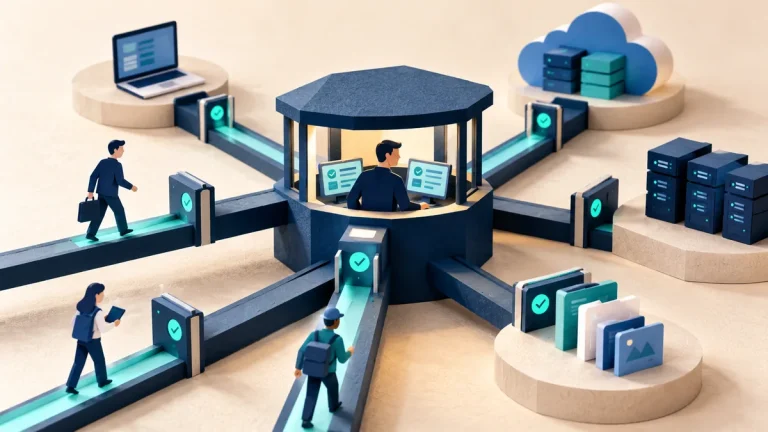
Being signed in does not mean a person should see every record in an application. Access control is the set of rules that decides what each user can read or change. A failure in those rules can expose another customer’s invoice, another employee’s file, or an administrator-only action.
Understand the idea
The application must check the requested record as well as the user’s identity. Hiding a button is not enough because a request can reach the server by another route. A long or hard-to-guess record number may reduce accidental discovery, but it does not replace a permission check.
- Identity
The service knows who made the request.
- Permission
It checks access to this record and this action.
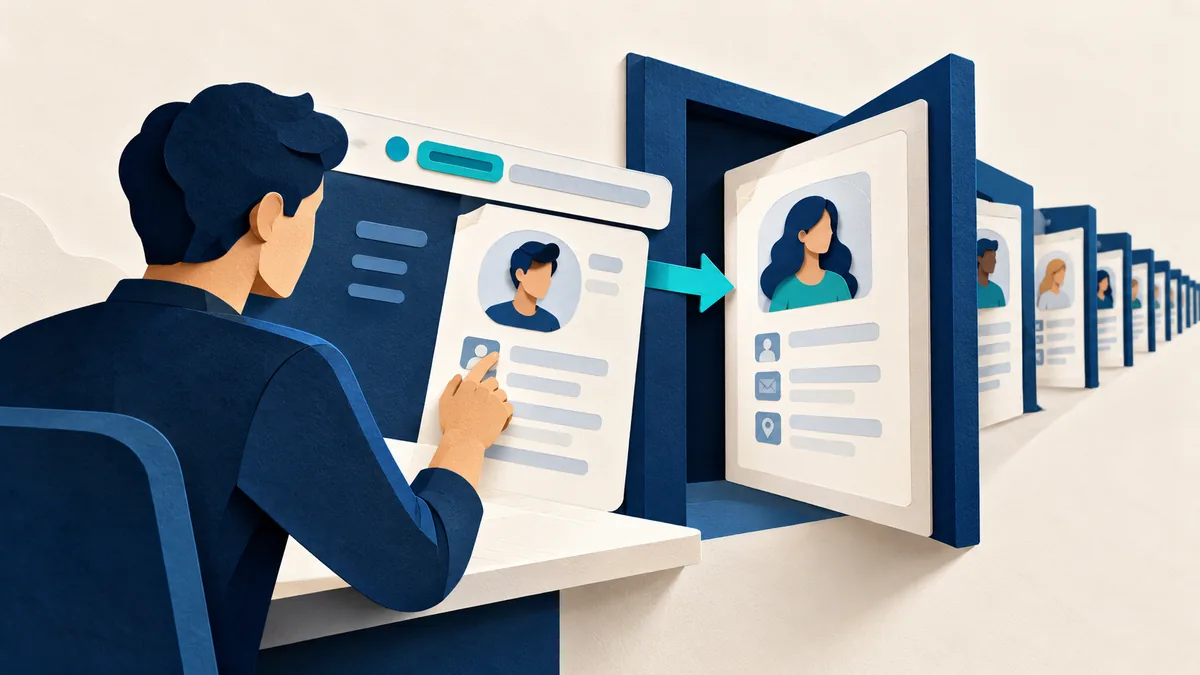
- Boundary
A different user’s record stays inaccessible.
A practical example
Suppose a donor portal lets one user download their receipt. In an approved test, the team uses a second account and asks whether it can access the first account’s receipt. The expected result is a refusal, even when the second account knows the receipt’s identifier.
What to do next
- Scope object queries to the caller's permissions. Check tenant membership, ownership, role, and relevant business state on the server.
- Default to denial. A missing policy or failed lookup should not become permission. Handle failures without leaking another customer's details.
- Control writable fields. Do not accept client-provided ownership, tenant, or privilege fields merely because they appeared in a valid request.
- Test alternate routes. Include mobile APIs, background jobs, file storage links, support tooling, and bulk actions.
How to check the result
Keep a small table of user roles, records, and allowed actions. Test both the actions that should work and those that should be refused after a change.
The record ID is difficult to guess. Is that enough?
No. Unpredictable identifiers can reduce guessing, but they do not replace server-side authorization. Test with accounts that have different access rights in an approved environment.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.