
Showing 13–24 of 24 articles
Page 2 of 2
Staging sites that are still open on the internet
A staging site can contain production data and powerful integration credentials. Keep its access and outbound behavior deliberately separate from the live service.
Read the visual guide
Treat domain renewal as a security control
An essential domain depends on working ownership, billing, recovery, and renewal arrangements. Check those dependencies while the service is healthy, not after it disappears.
Read the visual guide
Who should be allowed to change your DNS records
Control of DNS can affect email, websites, and other essential services. Identify the registrar, DNS host, privileged users, and applications that can change records.
Read the visual guide
Printers and cameras that still have an open admin page
An office appliance can hold credentials, send documents, and expose management features. Treat it as a managed system with an owner, support status, and limited access.
Read the visual guide
Work data on phones the company does not own
Bring-your-own-device arrangements need a clear boundary between work information and personal use. Agree what may be stored, what controls apply, and what happens on loss or departure.
Read the visual guide
What to do when a password is pasted into chat
Deleting a chat message does not invalidate a password or token that someone may have copied. Identify the credential, revoke or rotate it, and review its possible use.
Read the visual guide
Who should have administrator rights on a work laptop
Administrator access changes what software can do to a device. Limit routine privilege while giving staff a clear, workable route for approved installation and support.
Read the visual guide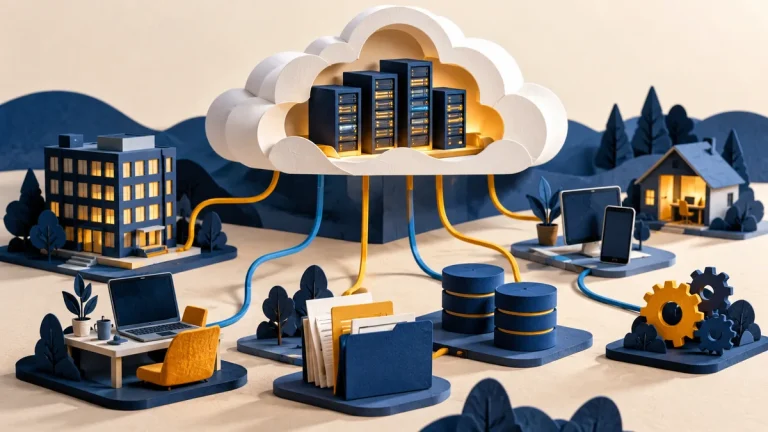
What you still have to secure when you use the cloud
A managed cloud service does not remove every security responsibility from your team. Map the provider’s role and your own configuration, identities, data, and recovery duties.
Read the visual guide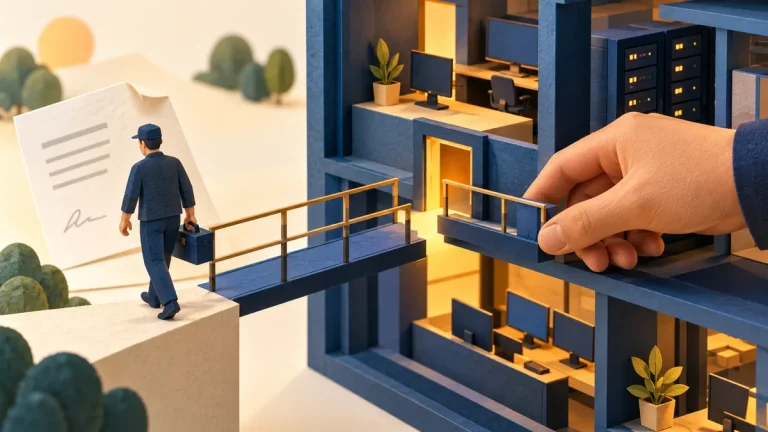
Close a vendor’s access when the contract ends
A contract ending does not automatically remove a supplier’s technical access. Use an access register to close named accounts, integrations, remote agents, and shared secrets.
Read the visual guide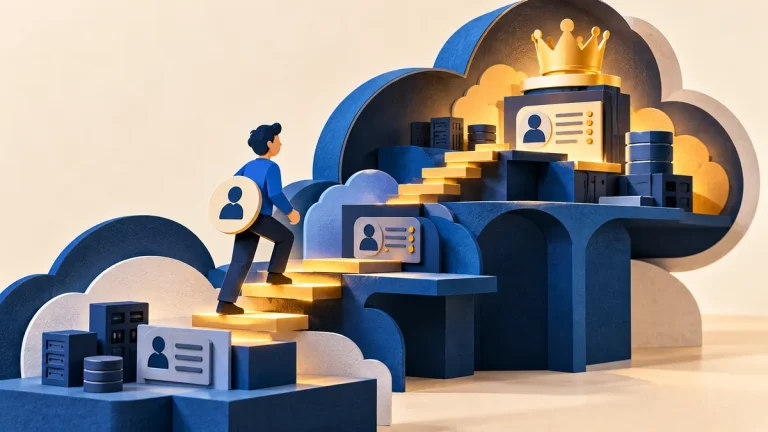
Cloud IAM escalation: when a small permission becomes admin access
A role can gain power indirectly by changing another identity, passing a privileged role, or altering a workload. Review what permissions make possible together, not only their individual names.
Read the visual guide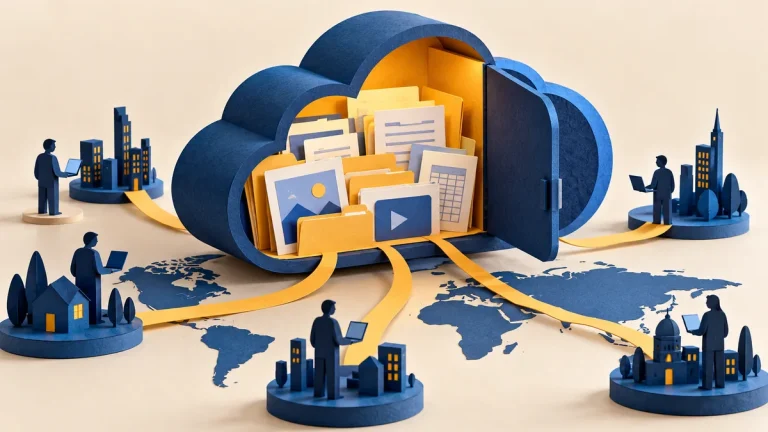
Public cloud storage: find exposed files and close access safely
A storage service can encrypt its data and still make it public. Review the paths to the files: identities, bucket or container policies, shared links, and any public delivery layer.
Read the visual guide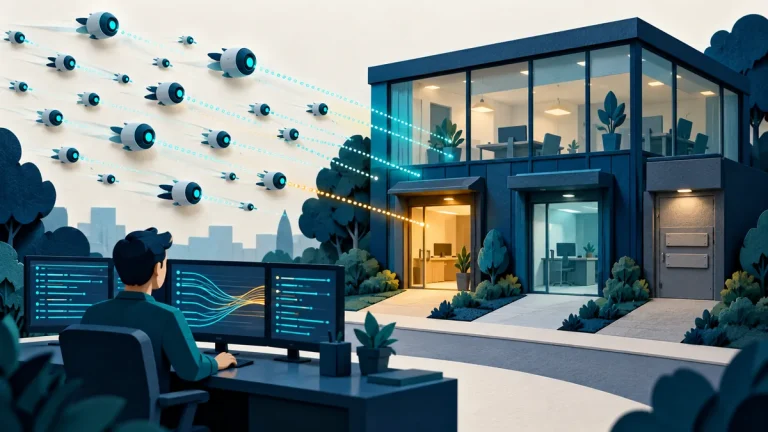
Website scanning bots: is it probing or a real breach?
A scan in your logs shows that someone asked a question. The response—and what happened next—tells you whether they reached something valuable. Start there before declaring a breach.
Read the visual guide