
Showing 25–35 of 35 articles
Page 3 of 3
How to roll out a password manager to a small company
A team vault needs an ownership model as well as an app. Decide what is personal, what the organization owns, and how access will be removed when someone leaves.
Read the visual guide
How to remove access when someone leaves
A person’s access may extend beyond their main account. Use a planned sequence to protect information, close sessions and tokens, and transfer legitimate ownership without losing critical work.
Read the visual guide
Close a vendor’s access when the contract ends
A contract ending does not automatically remove a supplier’s technical access. Use an access register to close named accounts, integrations, remote agents, and shared secrets.
Read the visual guide
What a browser extension can see, and which ones to remove
An extension’s permissions determine what it can observe or change. Keep the extensions you need, understand their access, and remove those that no longer have a clear purpose.
Read the visual guide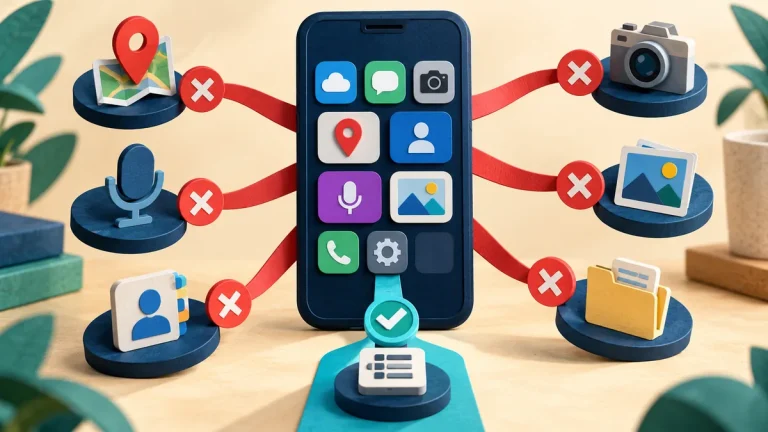
Which phone permissions an app does not need
A permission grants a real capability, such as reading contacts or using the microphone. Ask whether that capability is necessary for the feature you want to use.
Read the visual guide
Why a shared family password becomes a problem
A shared password makes it difficult to control access, recover accounts, and see who changed something. Prefer separate accounts and the service’s own sharing features.
Read the visual guide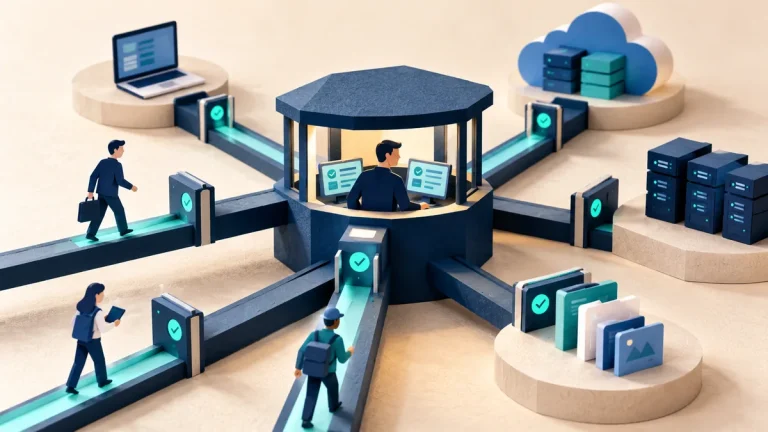
Practical zero trust: verify access to each important service
For a small team, zero trust starts with explicit access decisions around important services. Identity, device context, least privilege, and review matter more than adopting a label.
Read the visual guide
Cloud IAM escalation: when a small permission becomes admin access
A role can gain power indirectly by changing another identity, passing a privileged role, or altering a workload. Review what permissions make possible together, not only their individual names.
Read the visual guide
Public cloud storage: find exposed files and close access safely
A storage service can encrypt its data and still make it public. Review the paths to the files: identities, bucket or container policies, shared links, and any public delivery layer.
Read the visual guide
API business-logic abuse: valid requests can still cause harm
An API request can be correctly formatted and still misuse a workflow. Review the business outcome, especially repeated actions, ownership checks, and limits that span several requests.
Read the visual guide
Broken access control: can one user reach another user’s data?
Being signed in should not give a person access to every record. The server must check permission for the specific object and action on every request.
Read the visual guide