
Showing 1–9 of 9 articles
How to run a short security exercise with eight people
A short exercise can reveal whether people know who decides, who contacts whom, and how recovery would begin. Use a realistic scenario and finish with a small, owned action list.
Read the visual guide
How long a shared file link should stay open
A sharing link should serve a specific task and audience. Named recipients, suitable permissions, and an expiry date can reduce access that continues after the work is done.
Read the visual guide
How staff should report a suspicious email
People report more effectively when the route is easy to find and the response is clear. Ask for the message and what happened after it, without encouraging further interaction.
Read the visual guide
How to roll out a password manager to a small company
A team vault needs an ownership model as well as an app. Decide what is personal, what the organization owns, and how access will be removed when someone leaves.
Read the visual guide
How to remove access when someone leaves
A person’s access may extend beyond their main account. Use a planned sequence to protect information, close sessions and tokens, and transfer legitimate ownership without losing critical work.
Read the visual guide
How a team of five can patch without stopping the work
A workable patch routine names an owner, prioritizes exposed and important systems, and checks the affected workflow after an update. Keep exceptions visible rather than indefinitely postponed.
Read the visual guide
How a small team proves it can restore a backup
A backup job marked successful does not prove that people can resume work. Restore a representative sample into a safe environment and check the data, access, and dependencies.
Read the visual guide
What DMARC does for a small company’s email
DMARC connects your domain’s email authentication results to a published policy. A successful rollout starts with a complete list of legitimate senders and careful delivery checks.
Read the visual guide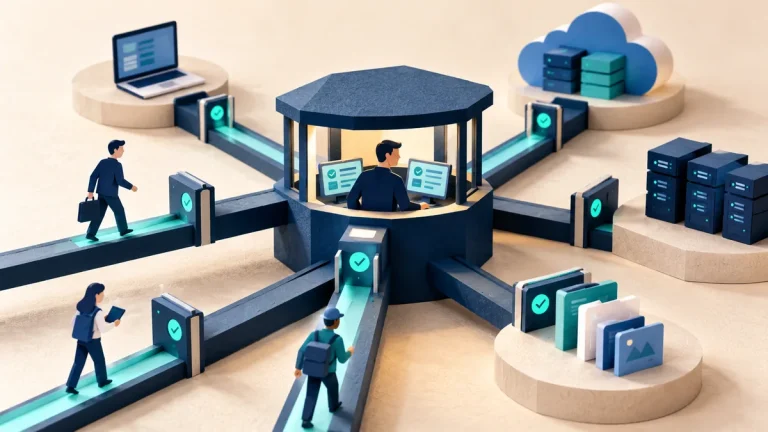
Practical zero trust: verify access to each important service
For a small team, zero trust starts with explicit access decisions around important services. Identity, device context, least privilege, and review matter more than adopting a label.
Read the visual guide