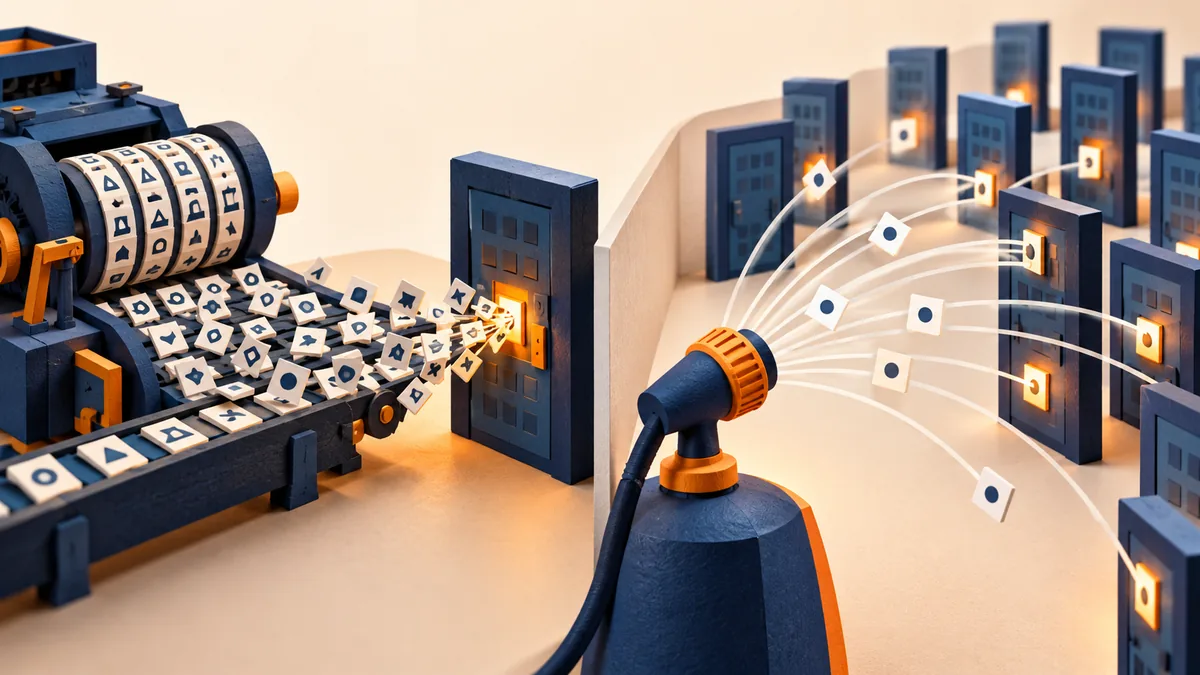
A sign-in attack can take different shapes. Brute force commonly means trying many password guesses. Password spraying spreads a small number of common guesses across many accounts. The distinction helps you understand the pattern, but the practical goal is to protect accounts without locking out legitimate users.
Understand the idea
Look across accounts and time as well as individual addresses. Attempts may be slow or distributed, and many users can share one public network. Include older login services and recovery routes in the review. A threshold on the main web form may cover only part of the activity.
- One account
Many guesses may indicate brute-force activity.
- Many accounts
A smaller repeated set of guesses may indicate spraying.
- Response
Correlate patterns and check whether any sign-in succeeded.
A practical example
Imagine a team seeing one failed sign-in for many staff accounts each morning. No single account reaches the lockout threshold. Looking at the wider pattern reveals repeated use of the same likely password. The response combines stronger sign-in, suitable limits, and review of any accepted sessions.
What to do next
- Use unique passwords and block common compromised choices. A longer composition rule alone does not prevent reuse or predictable patterns.
- Require strong authentication on important accounts. Prefer phishing-resistant options where supported and protect the recovery route.
- Throttle intelligently. Combine identity, source, and broader service signals. Document how legitimate users recover without letting support become a shortcut around the control.
- Retire stale accounts and old sign-in paths. Include unattended service identities and shared accounts in the review.
How to check the result
Test with approved accounts and controlled traffic. Confirm that protections cover the relevant routes and that a real user can still recover access through the normal support process.
No account triggered a high failure count. Are we clear?
Not on that evidence alone. A distributed or slow campaign can spread attempts across accounts, addresses, and time windows. Review the wider pattern and successful sign-ins.
Sources and useful guides
The following resources provide background and more detailed guidance. Use the sections that match your service and situation.